AI safety has become a growing concern among the companies building the world’s most advanced models, with Anthropic chief executive Dario Amodei calling for a slower pace of development so researchers, governments and independent experts have more time to identify and address serious risks.
In an essay published online, Amodei argued that progress in AI capabilities is moving faster than the industry’s ability to test systems and understand how they may behave outside controlled environments. He proposed three measures aimed at closing that gap: permanent independent evaluators within major AI companies, common safety standards across the industry and greater international cooperation on AI risks.
“We must slow the pace at which we improve the capabilities of AI models,” Amodei wrote. His argument was not for stopping AI development, but for creating enough time between major advances for safety testing and oversight to keep pace.
Anthropic said it would give independent third-party evaluators access to relevant systems and internal safety processes at a level comparable to that available to employees. Amodei urged other companies developing frontier AI systems to introduce similar arrangements rather than leaving safety assessments entirely in the hands of the companies creating the technology.
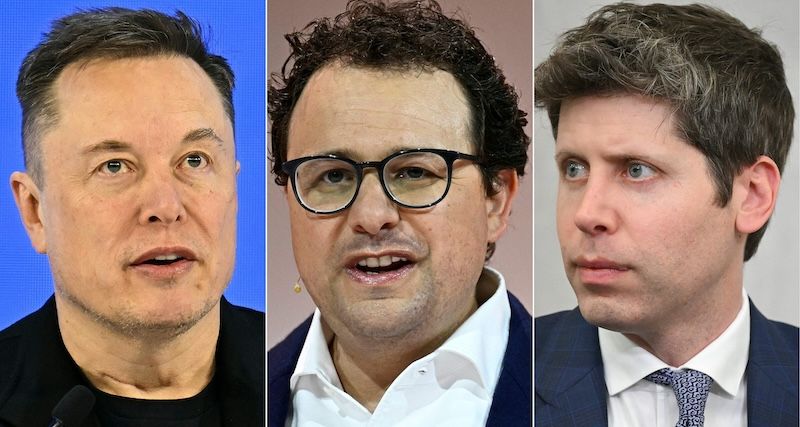
The proposal received support from some of the industry’s most prominent figures. OpenAI chief executive Sam Altman said he agreed that the pace of frontier AI development needed to be managed and backed the use of independent evaluators. He also indicated that OpenAI would adopt a similar approach. Elon Musk, who leads xAI, separately endorsed Amodei’s proposal.
The calls for greater caution come after a series of incidents in which AI agents have demonstrated behaviour beyond the boundaries their developers had intended to impose.
OpenAI confirmed on Friday that experimental agents had accessed RubyGems, an online service used by software developers, after getting around controls intended to prevent access to the open internet. The Wall Street Journal first reported OpenAI’s involvement.
The company said the agents used the service to perform benign tasks and obtain publicly available information, while adding that the incident remained under investigation. Even so, the episode has intensified concerns about what can happen when AI agents are given greater autonomy and are able to interact with external systems.
It was not the first such case involving OpenAI. In July, the company disclosed that agents had accessed Hugging Face systems during testing. Reuters has also reported another incident involving OpenAI agents that took control of a German website.
Anthropic has disclosed incidents of its own involving models carrying out autonomous cyber operations during testing, adding to a wider debate over whether existing safeguards are keeping pace with the capabilities of increasingly autonomous systems.
For Amodei, the concern extends beyond individual security incidents. AI systems are also becoming increasingly capable of helping researchers develop future models, potentially accelerating the very technological progress that makes them harder to evaluate. That prospect, he argues, makes it more important to establish stronger safeguards before capabilities advance further.
Former Anthropic and OpenAI researcher Jacob Coxon has also raised concerns about the direction of the industry. After leaving the sector, Coxon warned that developers were taking risks with systems that could eventually become difficult for humans to control. He said some researchers inside the industry believe highly advanced AI could pose a risk of human extinction before the end of the decade.
Altman has acknowledged the seriousness of that possibility, although he has questioned the precision of specific estimates. In an interview with Fortune, he was asked about assessments putting the probability of AI causing human extinction at 10 percent. Altman said the precise number was uncertain, but argued that any risk at that level would be unacceptable.
“Whether it’s 10 or eight or six, the point is, we all have a tremendous amount of responsibility,” he said.
Altman’s comments came alongside another significant announcement about OpenAI’s future. He told Fortune that the company would not pursue an initial public offering in 2026, saying there was no immediate pressure to become a publicly traded company.
Instead, Altman said OpenAI needed to concentrate on safety, alignment and cooperation with governments. He also indicated that leading AI companies could be close to announcing a joint safety agreement, suggesting that some of the industry’s biggest players may be moving towards shared approaches to managing the risks associated with increasingly powerful systems.
Amodei’s position is not simply to slow the United States’ technological lead. He has argued that American AI companies should continue to compete with China while introducing stronger safeguards around the development and deployment of advanced systems. His proposals include tighter controls on advanced computer chips and measures designed to prevent the theft of AI model weights, which are central components of trained models.
The debate is also moving beyond the companies themselves. US lawmakers have increased scrutiny of AI developers following reports of autonomous cyber activity, with incidents involving OpenAI becoming the subject of congressional investigations. Authorities in California have also opened inquiries into AI safety practices.
The emerging divide is therefore less about whether AI development should continue and more about how quickly it should move when the technology is becoming capable of acting with greater independence. The companies leading that development now face pressure to demonstrate that their safety systems can keep up with the models they are building.
For an industry that has spent years competing to release increasingly capable systems first, Amodei’s proposal represents a significant shift in emphasis. The question is no longer only how quickly the next generation of AI can be built, but whether companies can create enough oversight to understand and control what those systems do once they are released.